ERP that keeps up
Help your people spend less time waiting on the system and more time moving work forward.
Big enough to trust. Small enough to care.
Protect your information. Keep your people productive. Get more value from your technology. We combine a security-first mindset with practical improvements to the way your business operates.
Manufacturing · Legal · Medical · Financial · And more
Help your people spend less time waiting on the system and more time moving work forward.
Use zero trust principles and proven safeguards to protect the people, systems, and information your business relies on.
Reduce infrastructure cost and complexity. Make technology spending serve the business.
A slow system, an extra manual step, or an expensive setup can get in the way of a good day’s work. From a production floor to a professional office, we look at your people, processes, and security needs together.
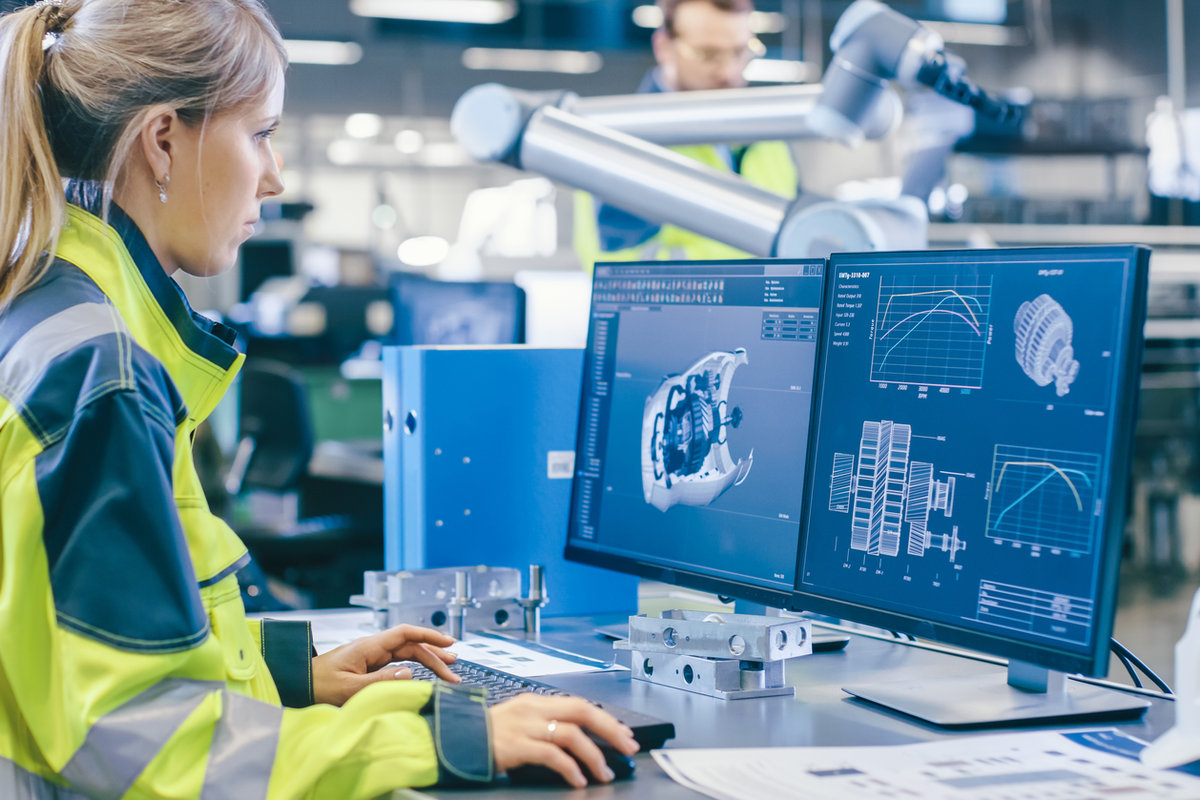
When your ERP system is slow, the whole business feels it. We help optimize ERP performance around the work your people need to get done.
Explore AIM ERP supportPut useful information where production happens. Connect people and equipment with access controls and network separation that respect the demands of your operation.
Talk about your production floorMake practical choices about what to keep, simplify, or change. Reduce overhead and overlapping tools while keeping security, recovery, and long-term support in view.
Talk about your infrastructureInstall, configure, and optimize AIM Vision ERP with infrastructure that fits the way you work. We support on-premises and cloud environments.
Plan a new AIM deployment or a move between on-premises servers and the cloud. Get the hardware, network, and configuration right from the start.
Track down server, storage, and network bottlenecks so your people can work instead of waiting on AIM. We optimize the infrastructure around the work your business needs to get done.
We understand electronic data interchange (EDI) and the links between your systems, production, and shipping. We troubleshoot performance in the context of the work it holds up.
Security should help your business move forward with confidence. We build around zero trust: access is verified, permissions are limited, and being inside the network does not automatically make a connection trusted.
Strengthen identity with multifactor authentication, least-privilege access, and device checks. Give people the access their work needs—not more.
Separate networks, harden configurations, patch systems, and protect endpoints. Reduce the ways a compromised account or device can affect the rest of your business.
Bring monitoring, actionable alerts, tested backups, and recovery planning together. Help your team recognize threats and know what to do when something goes wrong.
Our approach draws on industry best practices, including NIST zero trust guidance and the CIS Controls, with priorities matched to your risks, resources, and business needs.
We help defense contractors and suppliers achieve Cybersecurity Maturity Model Certification (CMMC), from scoping and remediation through audit preparation, assessment support, and resolving findings.
We also help protect technical data controlled by the International Traffic in Arms Regulations (ITAR) and implement safeguards required by Department of War (DoW) contracts.
Plan your CMMC certificationIdentify Federal Contract Information (FCI), Controlled Unclassified Information (CUI), and the people, devices, systems, and providers that handle it. Confirm the requirements in your contract.
Review your current controls against the applicable requirements, including NIST SP 800-171 for relevant CUI environments. Build a prioritized remediation plan with clear responsibilities.
Help implement access controls, secure configurations, monitoring, and recovery measures. Connect technical changes with the policies and everyday procedures your team follows.
Organize your System Security Plan (SSP), permitted Plans of Action and Milestones (POA&Ms), and assessment evidence. Support your team during assessment and help resolve findings on the path to certification.
Your contract determines the required CMMC level and assessment path. Certification is based on the applicable authorized assessment. ITAR compliance is a separate export-control obligation. Check the official CMMC program guidance ↗
Show us how work moves through your business, where your people lose time, and what information you need to protect. We listen, identify the risks and friction, then agree on practical priorities. Your operation—not a product catalog—sets the direction.
Twenty years helping customers meet their evolving IT needs.
Manufacturing expertise and an approach that also fits legal, medical, financial, and other businesses.
We choose solutions and partners for the value they bring to your business.
Managed IT, cybersecurity, networks, and consulting, with on-site and remote support.
You do not have to be a manufacturer to work with RBS. We adapt the technology, security priorities, and support to how your business actually operates.
ERP performance, connected production, and dependable operations.
Confidential case files, controlled access, and reliable collaboration.
Sensitive patient information, secure access, and systems your staff can rely on.
Client data protection, accountable access, and business continuity.
Professional services, retail, and more. Start with your needs, not an industry label.
Our partner relationships support practical, security-focused solutions. We recommend the combination that fits your operation—not a one-size-fits-all stack.
 Gold Partner
 Premier Partner
 Reseller Partner
 Reseller Partner
 Bronze Partner
 Reseller Partner
 Reseller Partner
Open the RBS documentation platform.
docs.rbs-mi.comConnect when directed by your RBS technician.
help.rbs-mi.comA security concern, a CMMC requirement, or a system holding you back? We’ll listen and talk through a practical next step for your business.